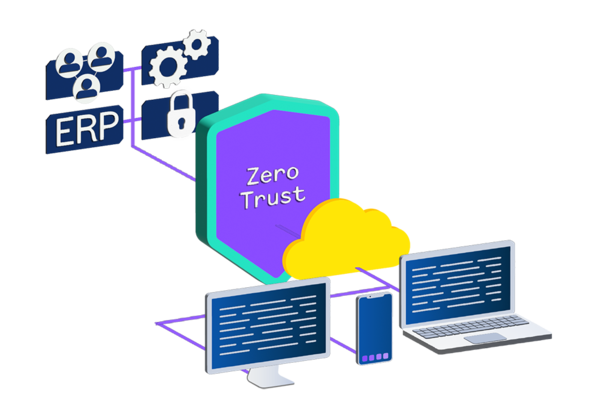
Internal applications must be accessible to authorized users without granting them full access to the network. Zero Trust Access takes an identity-centric approach: The system verifies each access request individually and grants access only to authorized applications. This allows you to protect internal resources, reduce the attack surface, and enable secure access for remote employees, external service providers, and business partners. Permissions can be managed at a granular level and tailored to your organization’s requirements through defined policies.
Your Benefits
Identity-based access rules down to the level of individual applications
Clientless access via standard web browser, regardless of device or operating system
Reduced attack surface through consistent access restriction
Integration with existing user management systems
Complementary Solutions
In sensitive infrastructures, both firewalls and data diodes are used. Unlike firewalls, data diodes transmit user data only in one direction, e.g. for data transfers from black to red networks or monitoring applications. An IDS/IPS such as cognitix Threat Defender also complements the protection of firewall solutions by establishing a second line of defense in the network.